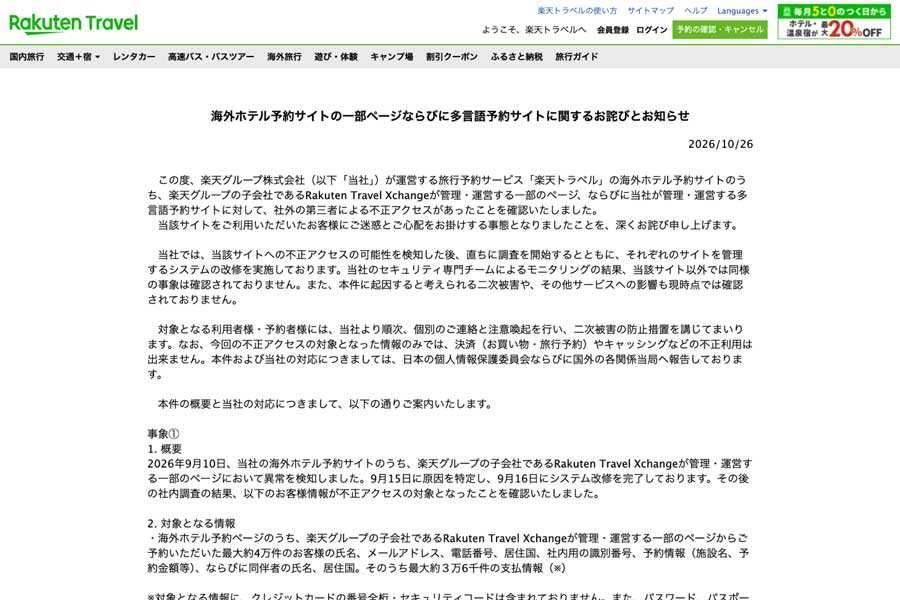
Rakuten Group announced that it has confirmed unauthorized access by a third party to certain pages of the overseas hotel booking website of its travel reservation service, Rakuten Travel, and to its multilingual booking website.
On certain pages of the overseas hotel booking website managed and operated by its subsidiary, Rakuten Travel Xchange, an anomaly was detected on September 10. The cause was identified on September 15, and system modifications were completed on September 16. The affected information included the names, email addresses, telephone numbers, countries of residence, internal identification numbers, and booking information (such as property names and booking amounts) of up to approximately 40,000 users who made reservations through the affected pages, as well as the names and countries of residence of their accompanying guests. Of these, payment information for up to approximately 36,000 users was also affected. The payment information included credit card issuer identification numbers and last four digits, cardholder names, expiration dates, and international card brand categories. It did not include full card numbers, security codes, passwords, identification document information such as passports, or addresses. In addition, the names, email addresses, telephone numbers, and internal identification numbers of up to approximately 2.6 million users who logged in to the affected pages were also affected.
For the multilingual booking website, the possibility of unauthorized access was detected on October 20. The cause was identified the same day, and system modifications were completed the following day, October 21. The affected information included the email addresses and internal identification numbers of up to approximately 860,000 users who logged in to the website, as well as the account names, email addresses, and internal identification numbers of up to approximately 40,000 accommodation facility employees entered through the administrative interface.
Rakuten has already blocked the access route and modified its systems, and has reported the matter to Japan’s Personal Information Protection Commission and relevant overseas authorities. According to monitoring by its security specialist team, no similar incidents have been confirmed on websites other than those affected. No secondary damage or impact on other services has been confirmed at this time.
The company also stated that the information affected in this incident alone cannot be used for fraudulent payment transactions or cash advances. Affected users will be contacted individually and provided with cautions on a rolling basis.